01 / Connected security tooling
Reconclave
A shared protocol and trust model for independent field devices and a desktop coordinator.
Protocol, architecture, device ecosystemExplore project ↗
THE WORK
From pocket hardware to assessment workflows. Explore the detailed case studies, then browse every public repository on my GitHub account.
Jump to all 41 repositories ↓SELECTED DEEP DIVES
01 / Connected security tooling
A shared protocol and trust model for independent field devices and a desktop coordinator.
02 / Assessment workflow
A scope-driven framework that turns scanning output into reviewable findings and reports.
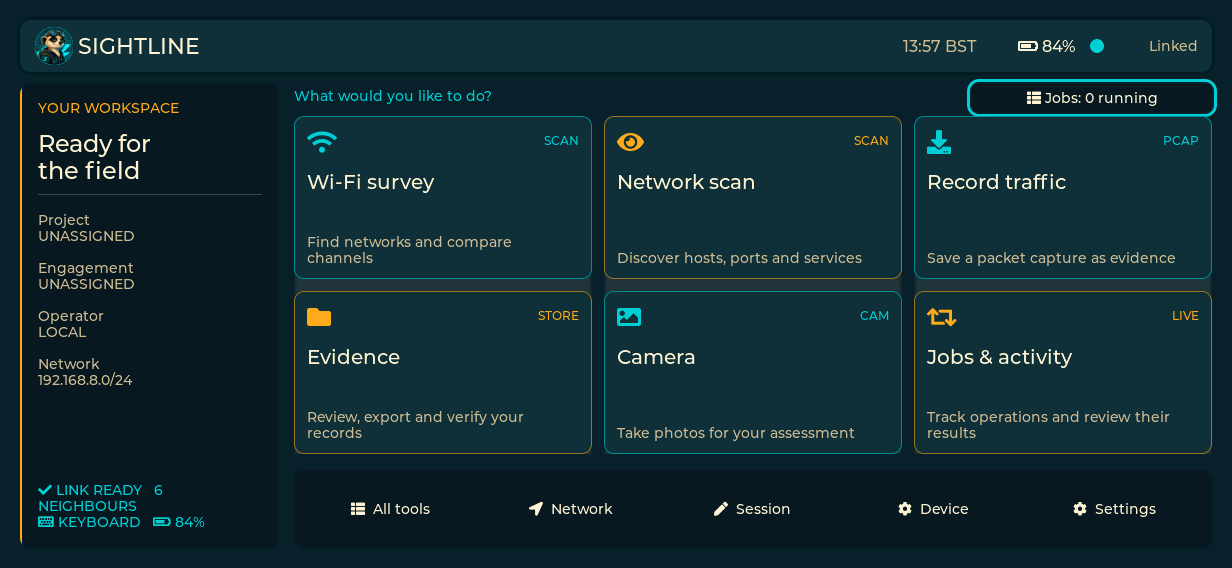
03 / Edge instrument
A touchscreen K230 field instrument for surveying, observing, and retaining evidence.
04 / Pocket field kit
A Cardputer ADV companion for local radio observation and authorised network scouting.
05 / Connected wearable
Custom watch firmware and an Android companion built around a real device and power budget.
PUBLIC GITHUB DIRECTORY
41 repositories · 33 original · 8 forks
This directory is a snapshot from 12 October 2026, including current projects, experiments, older work, and forks, ordered by most recent push. For the latest activity, visit my GitHub profile ↗.
Showing 41 repositories
Static-binary network segmentation assessment tool for authorised engagements.
Ragnar is a Powerful network scanning and offensive security tool for the Raspberry Pi with a 2.13-inch e-Paper HAT and is Father of Bjorn. It discovers network targets, open ports, exposed services, vulnerabilities.
Sift — an adaptive pentest framework: scope through recon, scanning, correlation and reporting.
Development-preview platform for authorised security assessment across a desktop coordinator and ESP32 device fleet.
A virtual pet that lives entirely on an ESP32-S3 — no app, no cloud, procedurally generated genome.
Pocket network and radio scout for the M5Stack Cardputer ADV — Wi-Fi/BLE/mesh recon with an on-screen Familiar.
LoRa Xtract — airgap data exfiltration over Meshtastic mesh radio, for authorised security demos.
Create authentic looking D&D homebrews using only markdown
A place for my D&D related stuff
Automated vulnerability scanning tool — Nmap + SSL scanning, plugin-extensible, Excel/HTML reports.
A creation of scripts devloped to get quick system information to aid in build reviews.
Bjorn is a powerful network scanning and offensive security tool for the Raspberry Pi with a 2.13-inch e-Paper HAT. It discovers network targets, identifies open ports, exposed services, and potential vulnerabilities. Bjorn can perform brute force attacks, file stealing, host zombification, and supports custom attack scripts.
A tool to review all notes in Obsidian through Ollama LLM and output to a new folder
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and physical engagements ... or into "A Little Offensive Appliance".
A place for my bash scripts to live. Feel free to take and edit.
Various scripts and codes
SecLists is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more.
No repositories match that search.